
France’s attribution of the supermarket‑refrigeration hacks to Iran isn’t just a headline — it’s a warning to every enterprise still treating OT security as a “later” problem.
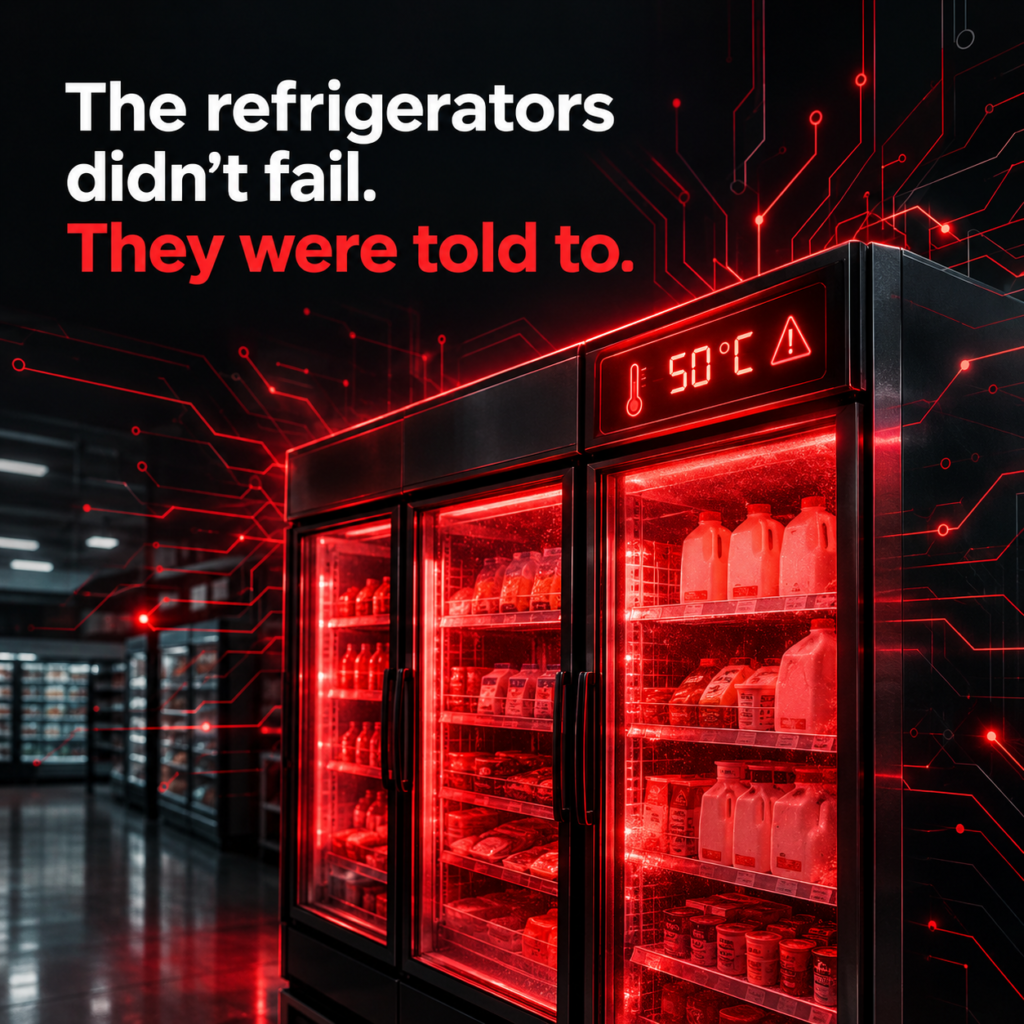
Attackers tied to Iran’s Islamic Revolutionary Guard Corps hijacked refrigeration controllers across 700 French retail sites, spiking temps to 50°C, causing fires and major losses. The same group hit blood banks, butcher shops, and hydroelectric micro‑plants across Europe. France called it “the first large‑scale sabotage cyberattack on French soil.” That’s a doctrine shift.
Here’s the uncomfortable truth:
OT isn’t adjacent to cyber risk — it is the frontline.
These everyday systems — PLCs, HVAC, cold‑chain units — are internet‑connected, poorly segmented, and often running outdated firmware. They’re easy targets with physical consequences.
This is the new playbook:
• Low‑complexity access paths
• High‑impact physical disruption
• Cross‑sector ripple effects
• Attribution‑ready signatures
And the implications are clear:
1️⃣ OT/IoT identity governance is now geopolitical.
2️⃣ “Air‑gapped” is a myth. Temporary connections become permanent attack paths.
3️⃣ Incident Response plans must account for physical‑world impact.
4️⃣ Nation‑states are shifting from espionage to sabotage.
5️⃣ Identity drift in OT environments is real — and dangerous.
If your org still treats OT as “someone else’s problem,” this incident should unsettle you. Not because France was attacked — but because the same attack surface exists in most enterprises today.
We don’t need more dashboards.
We need identity‑centric governance for machines, zero‑trust for controllers, and real‑time visibility into anything that can change a physical state.
The next campaign won’t target refrigerators. It’ll target whatever your business assumes is too trivial to matter.
🔍 Which physical‑impact system in your environment is easiest to compromise — and who owns securing it?
If you can’t answer that, the attackers already can.
Leave A Comment