
Your Attack Surface Doesn’t End at Your Firewall
The latest JPMorgan incident isn’t really a story about a bank.
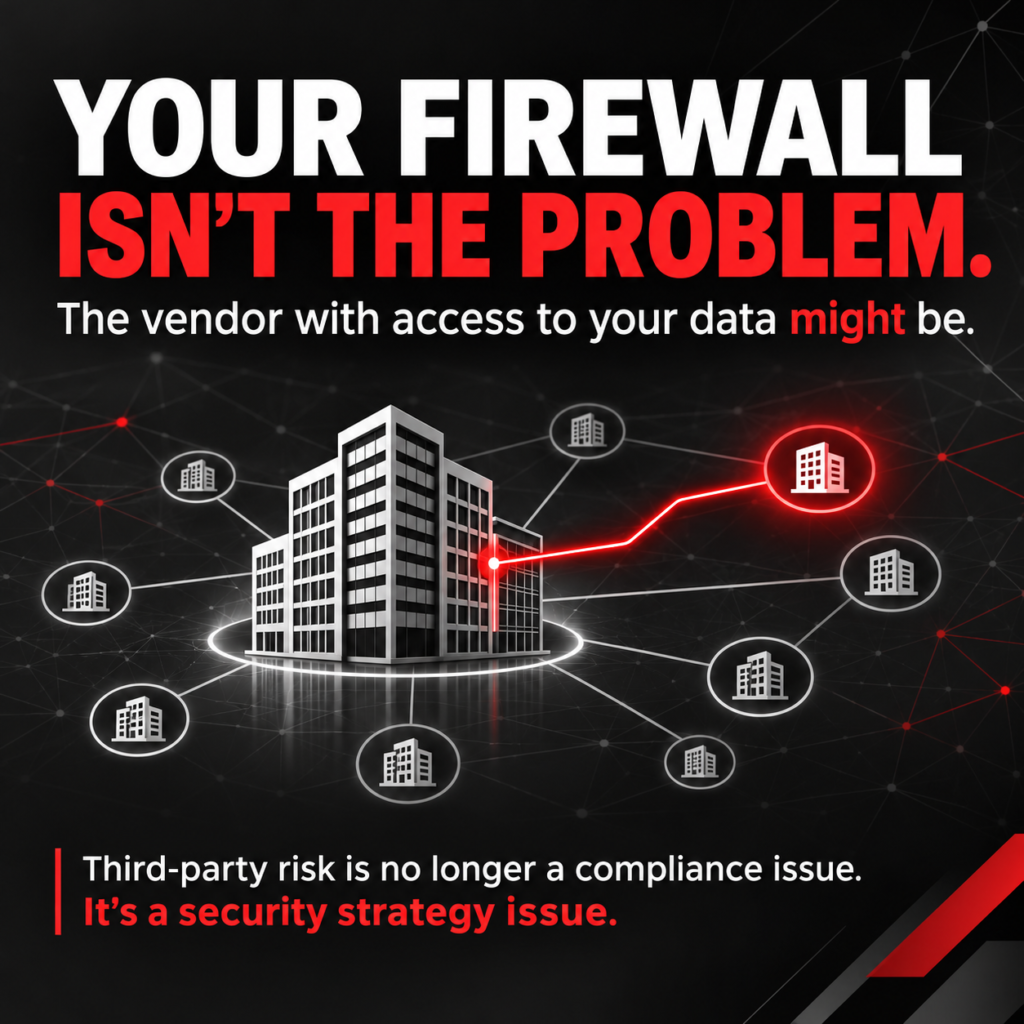
It’s a story about a cybersecurity model that many organizations still haven’t fully accepted: your security is only as strong as the vendors, platforms, and partners that touch your data.
For years, organizations have invested heavily in endpoint protection, identity security, network visibility, and employee awareness. Those investments matter.
But attackers have adapted.
Why spend months trying to breach a well-defended enterprise when a trusted third party may provide a faster, less protected path to sensitive information?
Too many organizations still treat third-party risk as a procurement exercise. A questionnaire. A compliance checkbox. An annual review stored away until renewal season.
Meanwhile, business dependency on external providers continues to accelerate.
The real challenge for security leaders isn’t protecting the systems they own.
It’s understanding, monitoring, and governing the systems they don’t.
That’s the uncomfortable reality of modern cybersecurity: organizations no longer operate as single entities. They operate as interconnected ecosystems.
And ecosystems create shared risk.
The companies that lead in the next decade won’t be the ones with the biggest security budgets.
They’ll be the ones that stop asking, “Are we secure?”
And start asking, “How secure is everyone we trust?”
Leave A Comment